Best Compliance Monitoring Software in 2026: 11 Platforms Compared
Compare the 11 best compliance monitoring software platforms for 2026. Discover features and find the right GRC tool for your security needs.
17 min readJaden Rose
Most companies pass their SOC 2 or ISO 27001 audit and then stop checking. The auditor's report covers a window that has closed, and the controls it describes start to slip the following week: an engineer opens a storage bucket to debug a release, or a contractor's login stays active a month after the contract ends. Compliance monitoring software catches those slips as they happen. It connects to the systems where your controls live, tests each one on a schedule, and tells a named percirson when a check fails.
The stakes rise for two reasons. First, the framework list keeps growing. A SaaS company that started with SOC 2 adds ISO 27001 to sell in Europe, then HIPAA when a healthcare customer signs, and every new framework means more controls to keep in shape. Second, enterprise buyers now ask for proof that your controls work today, and a report on last year's audit window doesn't answer that. Continuous monitoring gives you the current answer, and a trust center lets you show it.
The best compliance monitoring software for your team depends on two things: the frameworks you carry and how much help you want acting on alerts. All 11 platforms below keep security and privacy controls in check between audits. They differ in how much of that work they automate. Scytale comes first because its AI GRC platform treats monitoring as the program itself: controls stay tested between audits, and a failing check reaches an assigned owner with a GRC expert behind it.
Continuous compliance monitoring vs point-in-time audits
An audit is a sample. The auditor examines evidence from a set period and signs off, and the controls keep changing once fieldwork ends. A control that breaks in the third month of the next cycle can stay broken until someone samples it.
NIST set out the alternative in 2011. Its SP 800-137 guidance, written for federal systems, covers information security continuous monitoring. The publication describes a program that gives "visibility into the effectiveness of deployed security controls" and ongoing assurance that those controls stay in line with an organization's risk tolerance. The logic carries over to commercial frameworks.
Continuous compliance monitoring applies that model to SOC 2, ISO 27001 and the rest. Software connects to the systems that hold each control and tests them against an expected state, keeping a record of every pass and fail. Continuous control monitoring, or CCM, is the narrower term for that testing layer: automated checks on individual controls such as MFA enforcement or encryption at rest.
The gain is timing. A team that spots an open bucket on a Tuesday can close it that week. An auditor who spots the same bucket in a sample writes it up as an exception.
Where compliance monitoring sits next to compliance management and GRC
Vendors blur the three terms, so it helps to pin them down. Compliance monitoring is the watching: automated tests and the alerts they raise. Compliance management is the wider program around it, including policy work and audit preparation. GRC layers governance and enterprise risk on top, a fit for organizations with an internal audit function. Most platforms here span all three to some degree. Optro and LogicGate come from the GRC side, as does MetricStream, while Sprinto, Secureframe, Drata and Vanta grew out of compliance automation.
Different job, different tool
This list covers platforms that test security and privacy controls against frameworks like HIPAA, ISO 27001, PCI DSS and SOC 2. Searches for compliance monitoring also surface three other kinds of product, each made for a separate job, and none of them gets an entry below.
| If the job is | Look at | Example |
|---|---|---|
| Scanning cloud configurations against security benchmarks | Cloud security posture tools (CSPM and CNAPP) | Microsoft Defender for Cloud |
| Tracking new laws and edits to regulator websites | Regulatory-change monitors | Visualping |
| Watching healthcare, workforce or ethics duties | Industry and corporate compliance tools | symplr, for healthcare compliance |
The categories connect more than they compete. Scytale's integrations directory lists AWS Config, GuardDuty and Inspector alongside Microsoft Defender for Cloud. On endpoints it names CrowdStrike and SentinelOne, so data from posture and endpoint tools can feed its evidence collection and monitoring. MetricStream, further down the list, folds regulatory-change tracking into its compliance product.
How this list was compiled
The 11 platforms come from 19 ranking lists that surfaced for compliance monitoring searches in September 2026, narrowed to tools that test security and IT controls. Monitored systems and stated test cadence come from each vendor's own documentation, checked in September 2026. The review column draws on G2's summaries of praise and complaint themes, captured between June and September 2026, with mention counts as G2 reports them.
There was no hands-on testing. Every claim about a product traces to its vendor's pages or to G2 data, and nothing here reports a measured result. Where a vendor's pages don't name a monitored system or a schedule, the matrix further down says "not stated" and leaves the question for a demo.
11 compliance monitoring tools, platform by platform
Every profile starts with what the platform is and what it watches. A three-column snapshot follows, then a note on pricing and one documented drawback.
1) Scytale
Scytale is an AI GRC platform that tests controls around the clock and sends a real-time alert when one drifts out of compliance. Its AI GRC agents collect evidence from 150+ integrations and validate each item against control requirements, and controls cross-map across 80+ frameworks to cut duplicate work. Failing checks come with suggested remediation and dedicated GRC expert support, and a customizable Trust Center shows buyers current control status.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Cloud and identity controls, tested 24/7Endpoints and code repositoriesTraining completion and policy sign-offsVendor risk and regulatory change | Security and IT teams carrying several frameworks, from startups to enterprise, that want continuous compliance between audits and expert help when a test fails. | "Helpful" leads the praise tags on G2 with 146 mentions (4.8 out of 5 from 700+ reviews). |
Scytale sells tiered plans for startups through enterprise and prices them by custom quote rather than on its site. Some advanced capabilities only come with higher-tier plans.
2) Hyperproof
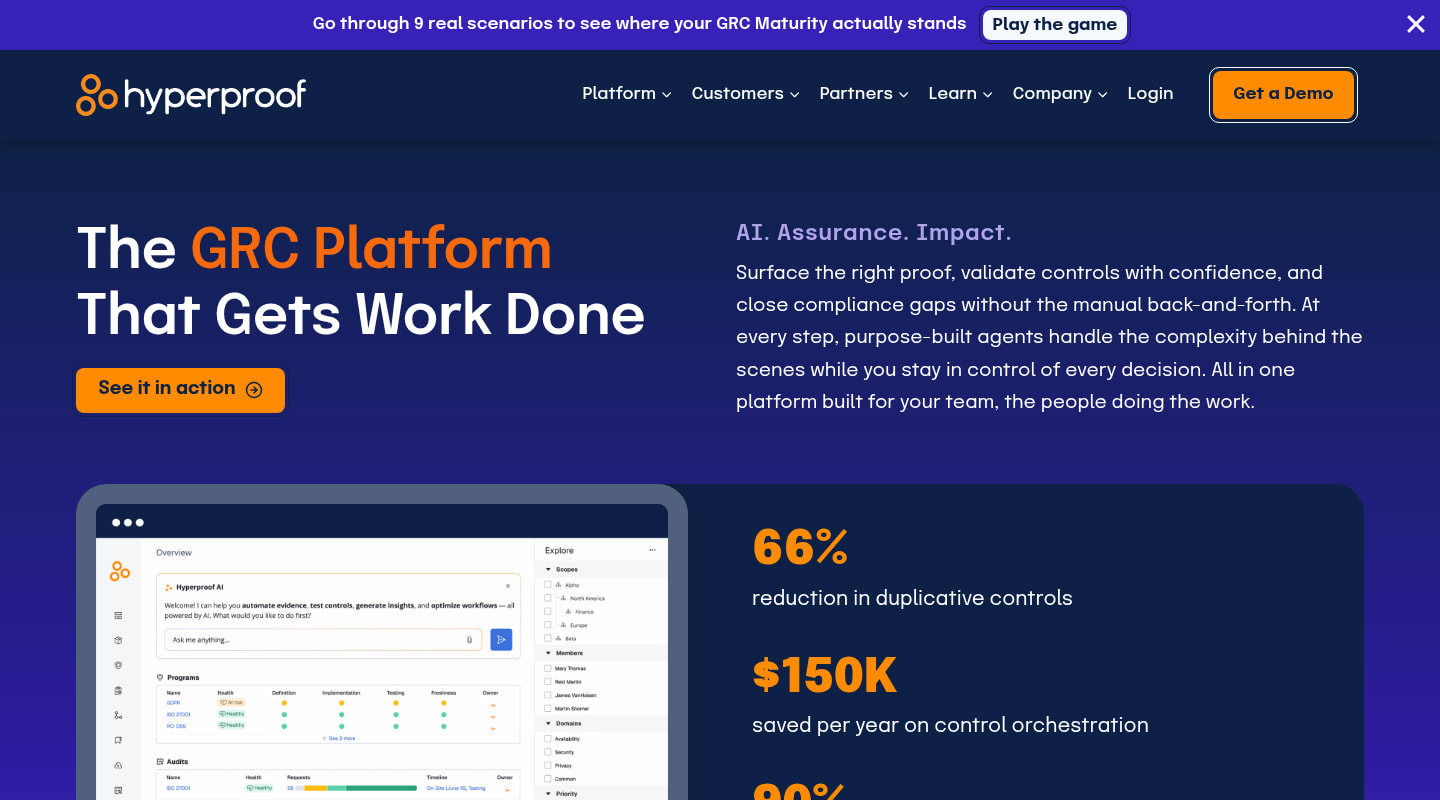
Hyperproof is a GRC platform that organizes compliance around a common control set and syncs evidence on demand or on a cadence the team picks. Its Livesync feature re-imports a file from cloud storage whenever the source changes. Risk registers draw on the same control-health data.
| What it monitors | Suited to | Review signal |
|---|---|---|
| AWS and Azure cloud connectorsIdentity and device-management integrationsHR data, including ADPVendor risk | Compliance operations teams running many frameworks who want to set evidence timing themselves. | Evidence management and collaboration draw the most praise on G2 (67 mentions; 4.5/5 from 217 reviews). |
The complaint G2 users raise most concerns how hard the advanced features are to learn (17 mentions). Budget onboarding time for the admins who'll configure its connectors.
3) Sprinto
Sprinto, a compliance automation vendor, links to six kinds of system, cloud and HR among them, and updates evidence as those systems change. It also watches supplier breach alerts. AI-assisted mapping ties each control to frameworks and policies.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Cloud and identity configuration changesCode repositories and devicesHR systemsVendor posture, including breach alerts | Cloud-first SaaS companies that want evidence kept current with little hands-on upkeep. | Ease of use backed by deployment support leads its G2 praise (384 mentions; 4.7/5 from 1,685 reviews). |
Sprinto structures plans around included frameworks and features, and its pricing page shows no dollar amounts. On G2, the most frequent complaint concerns integrations that misbehave with some niche tools (71 mentions).
4) Secureframe
Secureframe's compliance automation platform checks compliance status every day and emails admins when a test fails. It pulls CVE data from connected tools without an agent. It also spots new hires in HR tools and prompts them to finish training and accept policies.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Cloud misconfigurationsVulnerabilities, through CVE dataNew-hire training and policy acceptanceVendor risk | Teams that want a daily read on test status plus reminders for recurring tasks such as quarterly access reviews. | Integration trouble with niche tools tops the G2 complaints (184 mentions; 4.7/5 from 826 reviews). |
Secureframe's pricing page lists packages without dollar figures. Reviewers also ask for more control over the timing of follow-ups and schedules (141 mentions).
5) Scrut Automation
Scrut Automation runs hundreds of prebuilt compliance tests across your tech stack and flags gaps in real time. Teams can set how often each check recurs. An employee module adds tailored security training and continuous device compliance checks.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Controls across the connected stackDevice complianceEmployee security trainingAccess reviews and vendor risk | Growing teams that want prebuilt tests and close vendor support through setup. | Ease of use and implementation earn the most G2 praise (276 mentions; 4.9/5 from 1,312 reviews). |
On G2, users describe bugs and broken workflows getting in the way of tracking (52 mentions). For a tool whose core job is tracking, that theme deserves a close look during a trial.
6) Optro (formerly AuditBoard)
Optro, the rebranded AuditBoard, is an enterprise GRC platform with ready-made continuous monitoring templates for standard IT controls. AI helps with gap assessments and control mapping. Controls and evidence carry across auditable entities, and the compliance module connects to Optro's audit and risk tools.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Standard IT controls, via monitoring templatesControl self-assessmentsEvidence shared across auditable entities | Internal audit and enterprise risk teams that want IT control monitoring inside a wider audit program. | Ease of use across its audit tools and modules is the top G2 praise theme (243 mentions; 4.6/5 from 1,596 reviews). |
The largest G2 complaint theme describes limited functionality and restricted access to analytics (71 mentions). Teams that report on monitoring results should test the dashboards they'll need.
7) OneTrust Tech Risk & Compliance
OneTrust Tech Risk & Compliance is the security compliance module in OneTrust's privacy and GRC suite. It gathers evidence through pre-architected collectors and keeps an evergreen asset inventory. It ships 55+ ready-to-use frameworks, and scoping surveys generate matching controls and evidence tasks.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Tech-stack evidence via pre-architected collectorsAsset inventoryPolicy access and attestations | Enterprises that want security compliance in the same suite as their privacy and third-party programs. | Users on G2 credit its centralized platform for ease of use (13 mentions; 4.6/5 from 108 reviews). |
G2's most common complaint is a complex implementation that needs time and planning (6 mentions).
8) LogicGate
LogicGate is a no-code GRC vendor whose Controls Compliance solution automates evidence tasks and adds AI control testing. It cross-maps controls across dozens of frameworks. A separate Regulatory Compliance Management solution handles rule changes.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Evidence collection tasksAI control testingRegulatory change, through a separate solution | Organizations with in-house GRC staff who would rather build their own workflows than adopt a prebuilt program. | Ease of use and flexibility lead the G2 praise (24 mentions; 4.6/5 from 191 reviews). |
G2 reviewers describe a steep initial setup (5 mentions) that gets harder without prior GRC experience (4).
9) MetricStream
MetricStream is an enterprise compliance platform that tracks regulatory change and maps each update to the controls and policies it affects. Teams test controls with designed tests or with self-assessments that go out as surveys. Dashboards let users drill into control status.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Regulatory changePolicy portal and attestationsControl tests and self-assessments | Large, regulation-heavy enterprises tracking obligations across many jurisdictions. | Only one G2 review, too few to read a pattern from. |
MetricStream's product page describes testing through designed tests and questionnaires. It names no automated links to cloud or identity systems.
10) Drata
Drata's platform re-runs control tests on a recurring schedule and keeps each pass or fail as history for auditors. Custom connections bring homegrown and on-prem systems into testing. Codebase tests catch issues while code is still in development.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Connected business systemsCodebase, during developmentPersonnel and policiesVendor risk | Engineering-led teams that want a test history and compliance checks inside the development pipeline. | Responsive support is the praise G2 users repeat most (135 mentions; 4.7/5 from 1,331 reviews). |
Drata prices by quote. Its G2 summary flags the configuration process and the auditor experience as areas that need work (35 mentions).
11) Vanta
Vanta automates compliance with more than 1,400 tests that run every hour through its integrations. Controls cross-map across 35+ frameworks. Personnel tools cover security training plus onboarding and offboarding.
| What it monitors | Suited to | Review signal |
|---|---|---|
| Cloud, identity and endpoint toolsSecurity training and background checksEmployee policy acceptanceVendor risk | Companies that want a large integration catalog and an in-app roadmap that walks them toward the audit. | An easy-to-use interface gathers the most G2 praise (675 mentions; 4.6/5 from 2,728 reviews). |
Vanta sells by quote, and its plans page lists no dollar amounts. The biggest G2 complaint theme covers integration problems that leave manual work behind (179 mentions).
What each platform monitors, and how often
Every vendor above describes its monitoring as continuous. Their product pages differ far more on two details: which systems the checks reach and how often they run. The matrix records what each vendor documents about both.
| Platform | Cloud | Identity | Endpoints | People (HR) | Code | Vendors | Regulatory change | Stated cadence |
|---|---|---|---|---|---|---|---|---|
| Scytale | Documented | Documented | Documented | Documented | Documented | Documented | Documented | 24/7 |
| Hyperproof | Documented | Documented | Documented | Documented | Documented | Documented | not stated | On demand or a cadence the customer sets |
| Sprinto | Documented | Documented | Documented | Documented | Documented | Documented | not stated | Real time, every day |
| Secureframe | Documented | not stated | not stated | Documented | not stated | Documented | not stated | Daily |
| Scrut Automation | Generic | Documented | Documented | Documented | not stated | Documented | not stated | Real time, with set recurrence intervals |
| Optro | Generic | not stated | not stated | not stated | not stated | not stated | not stated | not stated |
| OneTrust Tech Risk & Compliance | Generic | not stated | not stated | Documented | not stated | Documented | not stated | not stated |
| LogicGate | Generic | not stated | not stated | not stated | not stated | not stated | Documented | not stated |
| MetricStream | not stated | not stated | not stated | Documented | not stated | not stated | Documented | not stated |
| Drata | Documented | not stated | not stated | Documented | Documented | Documented | not stated | Recurring |
| Vanta | Documented | Documented | Documented | Documented | not stated | Documented | not stated | Every hour |
Source: vendor product and integration pages, checked September 29, 2026. Documented means the page names that surface; Generic means testing without named systems; not stated means the pages don't say.
Seven of the 11 publish a cadence of some kind. The wording varies, with Vanta's tests every hour at one end and Hyperproof's customer-set schedule at the other. Optro, OneTrust, LogicGate and MetricStream state none on their websites, which fits their audit and GRC focus.
Coverage also thins away from infrastructure. Identity and endpoints each appear on five vendors' pages, and code on four. Regulatory change shows up on three, two of them enterprise GRC tools. Scytale's pages document all seven surfaces along with a 24/7 cadence, and Hyperproof and Sprinto each document six.
As a shortlist for security and IT teams, four platforms document at least five surfaces plus a cadence: Scytale, Hyperproof, Sprinto and Vanta. A not-stated cell reflects silence on the vendor's pages rather than a missing feature, and a demo can settle it.
How to choose continuous control monitoring software
Use the matrix to build a shortlist, then test the rows that matter to you in a demo with your own systems connected.
Frameworks these tools monitor against
Most security and IT buyers arrive with SOC 2 or ISO 27001 on the calendar, and the two finish in different places. SOC 2 produces an auditor's attestation report, while ISO 27001 leads to a certification. HIPAA and PCI DSS add obligations for teams that handle health records or card data, and GDPR does the same for personal data. NIST SP 800-53 counts as a compliance standard in the sense most buyers mean. NIST describes it as a catalog of security and privacy controls, and it publishes crosswalks to ISO 27001 and to its own Cybersecurity Framework.
Check that each framework you carry sits in the vendor's library and that controls cross-map between them, so one test can serve several frameworks. Scytale cross-maps controls across 80+ frameworks, including AI governance standards such as ISO 42001, the EU AI Act and NIST AI RMF.
Check which systems the monitoring reaches
Cloud configuration is the easy part, and most vendors cover it. Ask each one to run live tests against your identity provider and HR system as well. A missed training deadline or a supplier's expired report can fail a control just like an open port. Connect the systems that hold your in-scope controls first; a tool wired to half the stack reports on half of it.
Decide who owns a failing check
Alerts help only when a named person acts on them. Drata shows ownership context next to each control's status, and Secureframe emails admins when a test changes state. Scytale's AI GRC agents attach remediation guidance to a failing check, and teams can tag the colleague responsible for the fix, with dedicated GRC expert support behind them.
AI features now reach further into that loop. Vanta generates code snippets for remediation, and LogicGate adds AI control testing. Treat any AI suggestion as a draft for a person on your team to approve.
Share monitoring status with buyers
Security questionnaires and procurement reviews ask for the same evidence a monitoring platform already holds. Scytale's customizable Trust Center draws its content from the compliance workflows running in the platform and stays in sync as they change. Vanta and Scrut Automation also offer trust center pages, so compare what each one can show without manual updates.
What drives the cost of a compliance monitoring system
None of the 11 vendors prints dollar prices on its website, so cost depends on the scope you ask them to quote. Two levers move it most.
Framework count comes first. Sprinto organizes its plans around included frameworks, and most vendors here, Scytale included, quote by the scope you bring. Vanta's own buying guide names users and integrations as further price drivers.
Services come second. Penetration testing and expert support can sit inside a plan or arrive as extra line items. Scytale offers GRC expert support and penetration testing alongside the platform, so ask which of them a quote covers.
Then price the hours. A platform that finds problems still needs people to fix them. Set the internal time your team will spend on alerts next to the subscription before comparing quotes.
Choosing compliance monitoring software that outlasts the audit
The best compliance monitoring software keeps a control tested through the months when nobody's auditing it, and it makes clear who fixes the control when it fails. The platforms here split into two groups. Automation-first tools test cloud controls on a published cadence, while the enterprise GRC suites document less about cadence and more about audit and regulatory workflows.
Scytale, an AI GRC platform, takes the first spot for security and IT teams. Its pages document round-the-clock monitoring across every surface in the matrix, and a failing check lands with an assigned owner who has GRC expert support to call on. Hyperproof and Sprinto document close to the same breadth, and Optro, OneTrust, LogicGate and MetricStream fit enterprises whose monitoring sits inside a larger audit or regulatory program. Expect stated cadence to become a standard line in vendor documentation as more buyers ask for it.
More in software
Venture
Write for entrepreneurs, founders, and builders.
Share startup lessons, growth tactics, and founder stories with readers on the same journey.
One free account across In Plain English, Stackademic, Venture, and Cubed.
How it works- Startups & entrepreneurship
- Marketing & growth
- Productivity & leadership
- Founder stories & lessons learned
Sign in
Google or GitHub
Complete profile
Takes a few minutes
Get approved & publish
Start sharing
Why write for Venture?
Entrepreneurship is rarely a straight path. The lessons worth sharing are learned while building.
Comments
Loading comments…